Penetration Testing Articles
What a good penetration test covers, what auditors look for in the report, and how automated, continuous and manual testing fit together.
8 posts
Why Your Annual Penetration Test Isn’t Covering Your AI Systems
Explore AI penetration test insights and discover how to secure AI applications from emerging vulnerabilities.
Why Your SaaS Penetration Test Might Be Testing a Product That No Longer Exists
Environment drift can make a clean SaaS penetration test meaningless. Learn how to scope tests that reflect real production risk.
Securing Biometric Payments: Why Ongoing Scanning and Penetration Testing Matter
Learn about the advantages of biometric payment security scanning in airports, banks, and retail environments for secure access.
Bridging the SOC 2 Gap: Why Auditors Need Independent Technical Testing
Explore the importance of SOC 2 penetration testing requirements for independent assessment of your cybersecurity defenses.
The VASP Cybersecurity Gap: Technical Testing vs Regulatory Audit Readiness
Find out why VASP cybersecurity compliance testing is crucial for aligning technical work with regulatory requirements for firms.
AI‑Accelerated Exploit Development & Continuous Pen Testing
AI is compressing patch windows from weeks to hours. Learn why continuous penetration testing is now the only realistic way to stay ahead of exploit development.
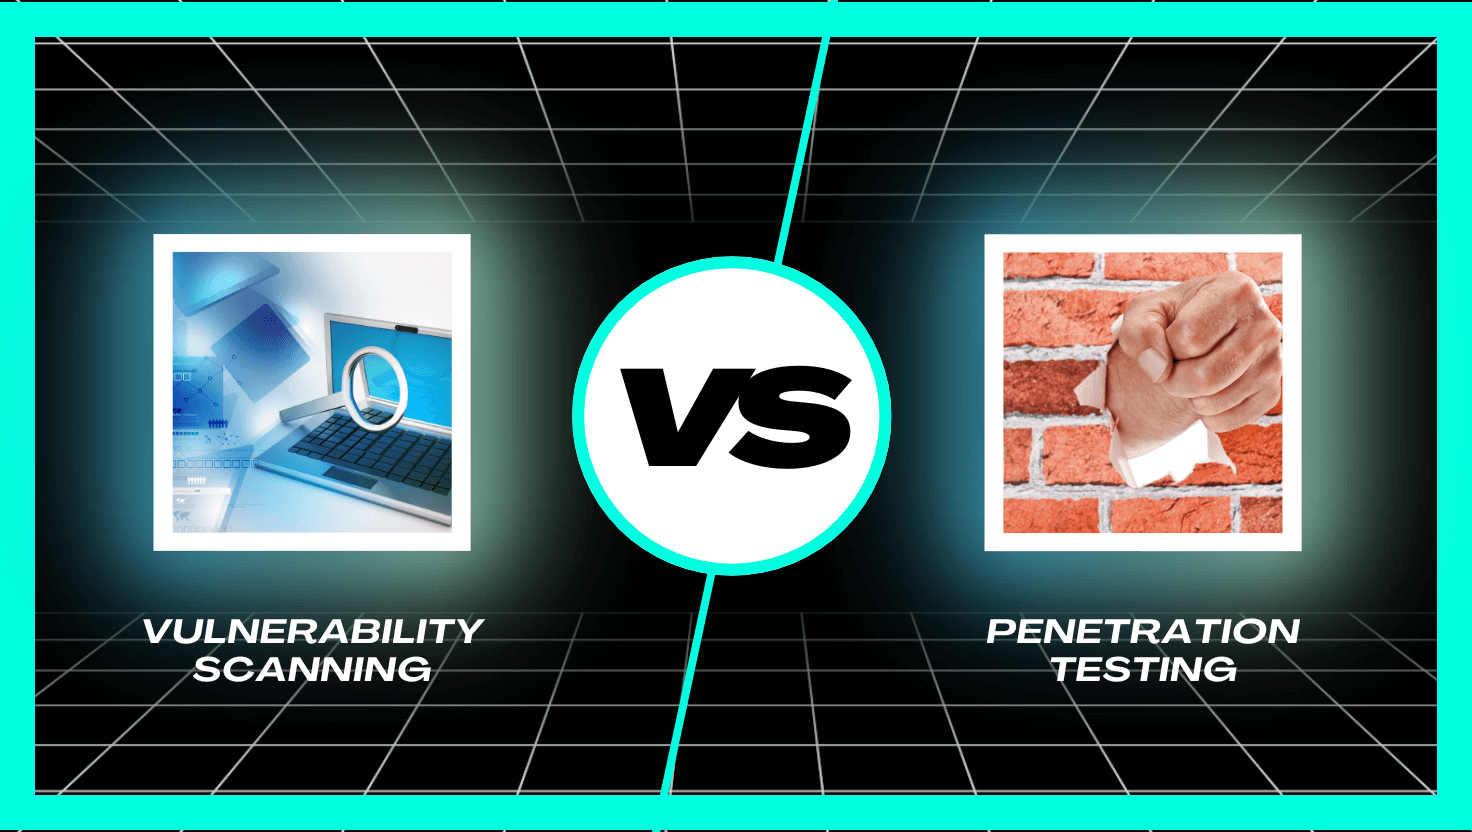
Penetration Testing vs Vulnerability Scanning: Why the Difference Matters
Penetration testing and vulnerability scanning are not interchangeable. Learn what each one actually does and how they combine into a defensible security program.
Ethical Hacking
Ethical hackers find your weak spots before criminals do. See how modern penetration testing fits into a security program and what results to expect.